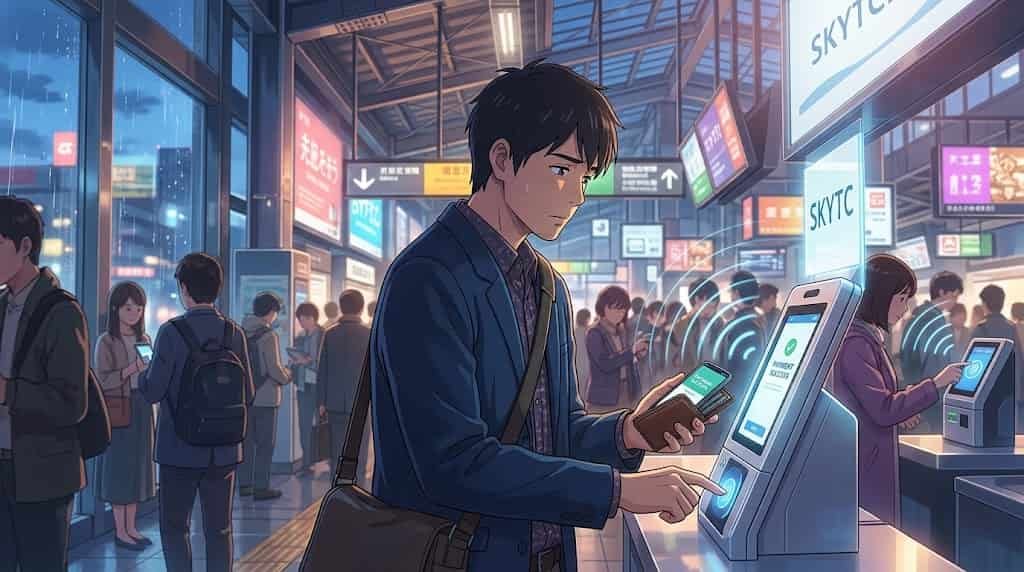
Learning how to stop contactless payment skimming risks is the tactical line between keeping your operational cash intact or watching your liquid balance evaporate in a crowded transit hub. High-frequency radio chips are embedded in every debit, credit, and smart card issued today, constantly waiting for an electromagnetic interrogation signal.
You are standing in line at an international airport or packed into a morning subway train, completely unaware that a bad actor with an amplified high-gain NFC reader is bumping past commuter pockets. The physical card stays in your wallet, yet your account experiences sudden unauthorized point-of-sale authorizations thousands of miles away.
When you shut down these radio-frequency attack vectors with real physical shielding and software-level isolation, you eliminate skimming vulnerabilities completely. You protect your liquid working capital, save countless hours fighting fraud claims with slow bureaucratic desk clerks, and lock down your daily transaction security forever.
The Core Equity Extract: Cash-Flow Snapshot
Here is the bottom line from the SkyTC security lab: static magnetic stripes and unshielded RFID cards in bargain-bin wallets are open invitations for data harvesting.
Modern EMV contactless transactions use dynamic one-time cryptograms, but raw physical card metadata, unencrypted identifiers, and relay-attack exploits can still leak account data to opportunistic threat actors.
The fix is fast: ditch naked physical cards, migrate daily spending to biometrically gated mobile wallets with hardware tokenization, and encase all legacy plastic in verified continuous Faraday cages.
Contactless Payment Skimming Risks: Hardware and Radio Protocol Matrix
To defend your daily cash flow, you have to understand the hardware layers operating at the 13.56 MHz spectrum. Here is how standard payment endpoints perform under real-world threat modeling:
| Payment Endpoint | Radio Architecture | Dynamic Cryptogram | Physical Proximity Vulnerability | Operational Security Rating |
|---|---|---|---|---|
| Naked EMV Contactless Card | Passive ISO/IEC 14443 | Yes (Single-use token) | High (Sniffable within range) | Low-grade baseline |
| Biometric Mobile Wallet | Active NFC with Secure Enclave | Yes (Device-specific DPAN) | Zero until user authenticates | Institutional tier |
| Wearable Payment Rings / Fobs | Passive RFID Tag | Varies by model | Moderate to High | Budget-friendly convenience |
| Physical POS Terminal Overlays | Modified Reader / Shimmer Tap | Bypasses display prompts | Direct physical tap | Compromised / High Risk |
How to Stop Contactless Payment Skimming Risks on Public Terminals
The biggest misconception in retail finance is assuming an encrypted chip makes you completely immune to walk-by exploitation. While modern chip standards generate dynamic authorization codes that stop simple static cloning, advanced attackers deploy proxy relay kits.
A relay kit uses two synchronized transceivers: one sits right next to your pocket on a crowded escalator, while the accomplice holds the second unit against a point-of-sale terminal at a high-end luxury counter. The terminal believes your physical card is directly touching the glass.
To break this attack loop, you need physical attenuation. You must starve the passive antenna inside the card of electromagnetic induction using solid conductive barriers, or bypass raw physical cards entirely using isolated mobile tokenization systems.
The Bare-Metal Trial: Pros, Cons, and Real-World Wear
Every defensive configuration comes with operational friction. Here is what you encounter when running hardened payment security across real field conditions:
Rigid Aluminum Faraday Card Sleeves
The Good: Continuous aluminum and copper mesh layers form an impermeable radio shield, dropping induced voltage from rogue readers down to absolute zero.
The Bad: Cheap composite sleeves delaminate after three weeks of pocket sweat, leaving edge gaps that destroy the radio shield while jamming card slots inside your wallet.
Tokenized Secure-Enclave Mobile Wallets
The Good: The device presents a virtual, tokenized device account number that never exposes your actual underlying master account or physical PAN to the terminal reader.
The Bad: If your battery drops to zero on a cross-border flight or your screen suffers a hard drop on the tarmac, you are locked out of your liquid capital until you reach power.
The Treasury Sheet: Cross-Border Capital Security
Point-of-sale hardware in international transit hubs, unattended toll booths, and outdoor automated fuel pumps is notorious for physical tampering. Criminal crews deploy ultra-thin “shimmers” directly inside the physical slot, paired with external wireless receiver taps snapped over the tap-to-pay housing.
These rigs look identical to factory retail hardware, but they capture raw terminal telemetry and relay transmission spikes back to nearby collection points.
Access the Federal Communications Commission (FCC.gov) for official device security protocols to verify compliance standards for localized short-range transmitters. In parallel, check your institutional background data on the Federal Reserve System (FederalReserve.gov) to track automated clearinghouse settlement risks, payment network dispute timeframes, and institutional liquidity velocity during multi-jurisdiction fraud events.
The Hypothetical Failure Scenario: The Transit Turnstile Sniff
Picture a digital nomad rushing through a crowded European metro terminal during peak morning rush hour. A physical debit card linked directly to a primary treasury checking account is sitting in the exterior mesh sleeve of a backpack for easy access.
An attacker standing by the turnstile carries an amplified, battery-powered NFC reader concealed inside a standard laptop bag. As the nomad squeezes through the crowded gate, the scanner closes the distance to a few centimeters.
The scanner triggers the card’s inductive loop, harvesting the cardholder name, structural token parameters, and expiring transaction histories. By lunch, the attacker leverages the unshielded metadata across compromised merchant gateways, triggering regional account freezes that leave the nomad stranded without liquid reserves in a foreign jurisdiction.
👇 Looking for more performance cheats? Check out our field-tested tactical blueprints:
The Hedging Protocol: Treasury and Liquidity Checklist
Run through this operational deployment checklist to seal every radio-frequency leakage vector across your financial stack:
- Stop contactless payment skimming risks with active Faraday shielding.
Expert Tip: Never trust soft fabric cases without continuous metal-mesh testing; inspect wallet seams under bright light for radio-leak gaps. - Migrate physical card spending to tokenized mobile apps.
Expert Tip: Apple Pay and Google Wallet never transmit your real card number, neutralizing static data sniffing even on unverified POS hardware. - Disable contactless functionality directly inside banking mobile apps.
Expert Tip: If your card issuer provides a software toggle for tap-to-pay, turn it off permanently on cards that stay inside your travel bag. - Isolate daily spending into a secondary buffer account.
Expert Tip: Never carry a debit card linked to your master liquidity reserve or business payroll accounts in public environments. - Enforce biometric authentication for all device transactions.
Expert Tip: Require mandatory fingerprint or facial scans on every single mobile tap to prevent unauthorized relay executions while your phone rests on a table. - Physically inspect standalone payment terminals before tapping.
Expert Tip: Give unattended POS bezels a firm physical pull; rogue overlay taps and shimmers snap off easily because they rely on temporary adhesives. - Set real-time push notifications for instant micro-transactions.
Expert Tip: Attackers test captured card metadata with microscopic charges first; receiving instant telemetry alerts lets you kill the card before heavy drains begin. - Keep legacy magnetic-stripe-only fallback cards completely disabled.
Expert Tip: Request modern EMV-only cards without unencrypted magnetic stripes to eliminate legacy swipe skimming at international merchant terminals. - Enforce zero-floor limits on physical business cards.
Expert Tip: Configure administrative card policies to require dual verification on any transaction executed outside domestic geographic boundaries. - Store backup plastic cards in dedicated metal cases.
Expert Tip: A solid aircraft-grade aluminum enclosure creates a zero-leak radio container that prevents accidental inductive wake-ups during transit. - Audit open merchant billing authorizations every thirty days.
Expert Tip: Clean out dormant subscription tokens and pre-authorized merchant holds from your account portal to minimize backend database exposure.
The Tax & FX Audit: No-Nonsense Cross-Border Answers
Can a stranger steal my entire card balance simply by walking past me?
No. They cannot clone an entire chip out of thin air, but an amplified reader can sniff metadata or execute an unauthorized relay charge if your card sits completely unshielded.
Do cheap RFID-blocking cards really protect an entire wallet?
Rarely. Most bargain-bin blocker cards only emit interference over a tiny physical radius, leaving cards on the outer edges of your wallet completely exposed to high-gain readers.
Are mobile wallets safer than physical contactless plastic cards?
Yes. Mobile wallets use hardware-isolated Secure Enclaves, generate rotating device tokens, and mandate biometric confirmation before the NFC radio will emit a single byte of data.
Can skimmers bypass the transaction limit on contactless cards?
Yes. Rogue relay attacks trick the network into processing transactions under merchant categories that bypass standard low-value contactless PIN prompts entirely.
Does wrapping a card in kitchen aluminum foil actually work?
Yes, as a temporary lab macete. A tight, unpunctured layer of standard aluminum creates a functional Faraday cage, though it tears apart after a few hours of physical friction in a pocket.
What is the difference between a skimmer and a shimmer?
Skimmers capture legacy magnetic stripe data on old reader housings, while shimmers are paper-thin circuit boards inserted into the EMV chip slot to record unencrypted terminal communication.
Can someone scan my payment card through a heavy winter jacket?
Yes. Standard fabric offers zero electromagnetic resistance against a 13.56 MHz interrogation wave broadcast by an amplified directional antenna rig.
What should I do immediately if I suspect my card was skimmed?
Freeze the card instantly inside your mobile banking app, report the unauthorized transaction trace, and request a fresh card with a new primary account number and token profile.
Read also: Safe Mobile Wallets Without Bank Accounts: The Sovereign Cash Protocol
RAW TREASURY WARNING: Unencrypted browser sessions, root-level smartphone exploits, and non-isolated software seed exposure create zero-day vectors for hardware token bypass exploits, session hijacks, and catastrophic capital drainage.